This week
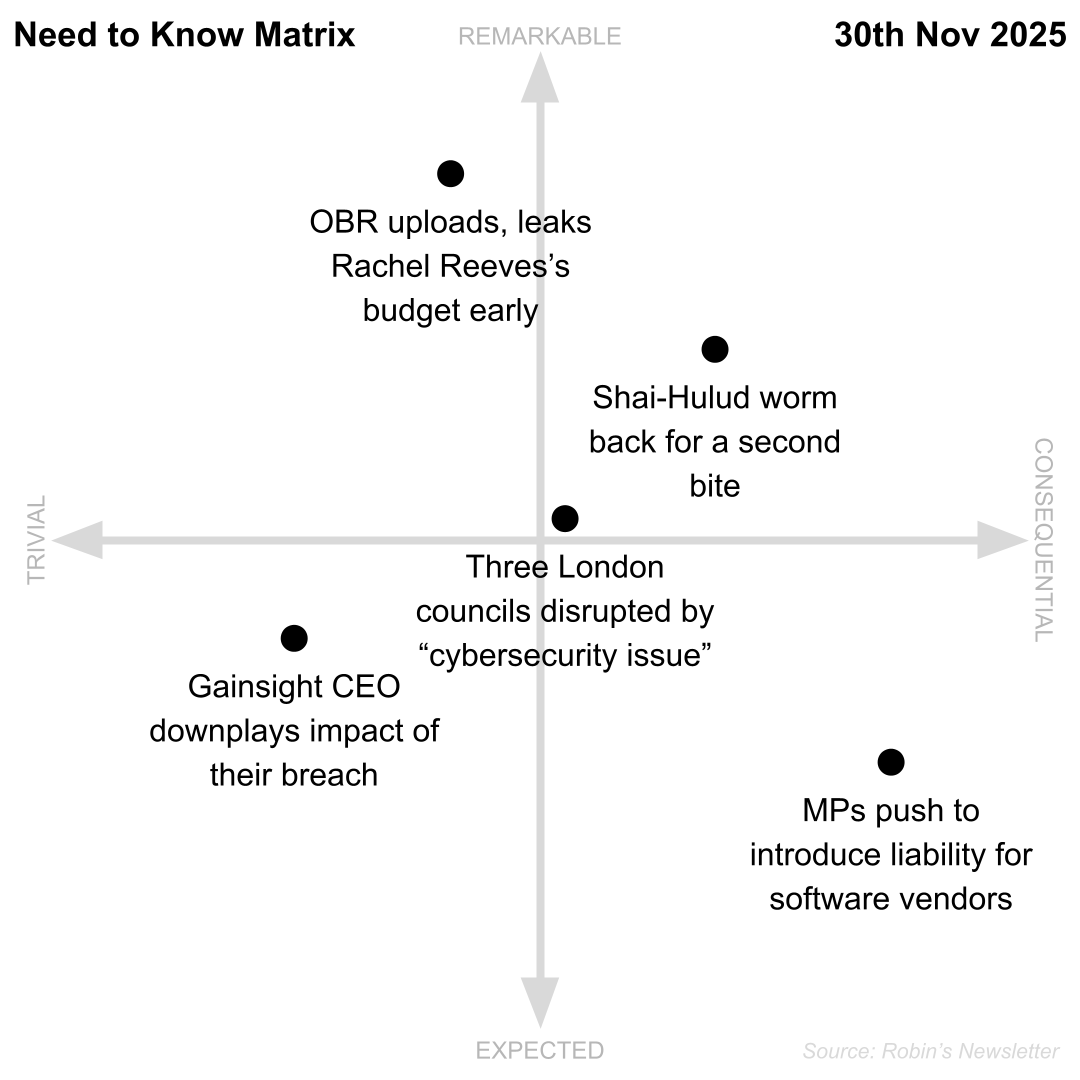
- Shai-Hulud worm back for a second bite
- Gainsight CEO downplays impact of their breach
- Three London councils disrupted by “cybersecurity issue”
- MPs push to introduce liability for software vendors
- OBR uploads, leaks Rachel Reeves’s budget early
Interesting stats
$262 million stolen by cybercriminals in ‘account takeover’ (ATO) fraud since January 2025, according to the FBI. LINK
£1.8 billion ($2.4B) price tag on the UK government’s digital ID scheme. LINK
Five things
-
Shai-Hulud, a self-replicating NPM worm, has resurfaced in a new wave of infections. More than 25,000 developers had their secrets and credentials for GitHub, NPM, AWS, Azure, GCP, and other CI/CD tools compromised over three days as the worm infected popular packages and copied itself into any NPM packages that those infected developers also maintained. Changes to this ‘2.0’ version of Shai-Hulud include a pre-installation phase and the ‘cross-victim exfiltration’ of secrets to public GitHub repositories owned by other users. SHAI-HULUD, REPORT
-
Gainsight CEO Chuck Ganapathi says that he’s only aware of “a handful of customers” that have been affected by the suspicious activity associated with the company’s Salesforce app. Google’s Threat Intelligence Group estimated that “more than 200” Sales instances had been affected. Both may be correct: Google’s number is for the number of tokens that have been compromised — and which may grant access to data — while Gainsight is referring to how many organisations have had their data pilfered by cybercriminals. Everyone seems to agree it’s likely Shiny Lapsus$ Hunters behind the breach, and the group is telling journalists that it was them, too. Understanding the extent of a breach is often time-consuming, made even more difficult in distributed environments or when breaches span supply chains. I’d expect the final number to take weeks to be known. GAINSIGHT
-
Three London councils have reported disruption after a “cybersecurity issue” with shared IT services. The Royal Borough of Kensington and Chelsea and Westminster City Council appear to have suffered the worst, with phone services disrupted. At the same time, the Borough of Hammersmith and Fulham shares some services but is taking “precautionary measures to review, isolate and protect our networks.” The three councils provide services to over 500,000 Londoners, and have enacted emergency plans and notified the National Crime Agency and NCSC. It sounds like ransomware, with teams working through the night this week to restore systems. LONDON, MORE
-
Members of Parliament on the Business and Trade Committee are pushing for increased liability for software vendors amidst “a huge increase in the private ownership of public risk.” The committee is calling on the government to take three actions to stem the economic threats to the UK, including: 1) introducing liability for software developers; 2) incentivising business investment in cyber resilience; and 3) mandatory reporting following malicious cyber incidents. Software liability intends to make vendors responsible for defects in their solutions, on the basis that it will drive up quality rather than have their customers bear the cost of poor security. SOFTWARE LIABILITY
-
The UK’s Office of Budget Responsibility (OBR), the arms-length public body tasked with providing independent economic forecasts and scrutiny over public finances, accidentally published its review of Rachel Reeves’s tax and spending plans 40 minutes before the Chancellor rose to the dispatch box in the House of Commons to deliver her budget. The budget is meant to be a closely guarded secret until formally announced. Markets reacted swiftly, and journalists scrambled to digest the plans. The OBRs had not linked to their report on any web pages; they had uploaded the file in preparation, and it followed the same filename convention as the previous year’s reports. Accessing it was a case of substituting the right digits. It’s an embarrassment for the OBR, which has drafted in former NCSC CEO Ciaran Martin as part of a review into what went wrong. OBR, MARTIN
Startup spotlight
As part of my pledge to support the UK cyber ecosystem, I’ll be featuring a different UK cyber startup each week.
This week it’s Cyberrock, a seed-stage business, building a minimum viable product:
- What do they do? Cyberrock is a solution that identifies vulnerabilities, tracks a live risk score, and enables or escalates clear, guided actions to stay secure.
- Who is it for? Small and medium businesses, and managed service providers who support SMEs.
- Where can you find out more? WEB, LINKEDIN
If you’re a UK-based cyber security startup interested in being featured in a ‘Startup Spotlight’ in my weekly newsletter, please fill out this form for consideration. It’s not a paid thing; just trying to support our ecosystem 🚀
In brief
-
⚠️ Incidents: SitusAMC, a US fintech that works with over 1,000 organisations, including JPMorgan Chase and Citigroup, has suffered a data breach affecting “accounting records and legal agreements”. At least a dozen juror websites made by Tyler Technologies exposed the names, dates of birth, home addresses, and more personal information of jurors because the unique ID for each juror was sequential and the login pages lacked rate-limiting protection. OpenAI says it was affected by an incident at analytics company Mixpanel, though no user chat or credentials were compromised. SITUSAMC, TYLER, OPENAI/MIXPANEL
-
🕵️ Threat Intel: KrebsOnSecurity has named Saif Al-Din Khader as Rey, one of the Scattered Lapsus$ Hunters (SLH) admins. Khader told Krebs that he is “already cooperating with law enforcement,” and “just want[s] to move on from all this stuff”. That’s going to paint quite the target on his back. Sticking with SLH… the group may be gearing up to target Zendesk customers, if domain registrations for typo-squatted domains are to be believed. SLH, ZENDESK
-
🧰 Guidance and tools: GreyNoise has released a checker to see if your IP address has been seen in any botnets. GREYNOISE
-
🛠️ Security engineering: Careful what you paste into web tools that format or beautify code: watchTowr say they’ve found lots of credentials, private keys, and API tokens amongst 8,000 pastes in services JSONFormatter and CodeBeautify. BEAUTIFY
-
🧿 Privacy: Over 70 civil liberties groups, academics, and legal experts are questioning the “collapse in enforcement activity” at the UK data protection watchdog, the Information Commissioner’s Office (ICO). Thailand bans Sam Altman’s Tools for Humanity from collecting iris scans. ICO, IRIS SCANS
-
📜 Policy & Regulation: The mobile industry group GSMA says differences in cyber regulations around the world are leading to higher compliance costs, with these slated to rise from the $15 billion to $19 billion range to between $40 billion and $42 billion by 2030. Comcast is settling a 2024 data breach affecting 270,000 customers with the Federal Communications Commission (FCC) for $1.5 million. GSMA (REPORT (PDF)), COMCAST
-
🗞️ Industry news: HP says it will lay off between 4,000 and 6,000 employees and save $1 billion in people costs by the end of 2028 as part of an AI usage pivot. Cyber insurer Beazley reported an 8% decline in gross written cyber premiums (top line revenue) in the first nine months to 30 September, citing “more claims,” which are “more expensive”. Competitors Chubb and AIG maintained or grew their revenues over the same period. Hacklore is a new site from industry veteran Bob Lord, aiming to combat ‘outdated’ advice, myths about public wifi, juice-jacking, and more that divert users’ attention from actions they can take to protect themselves better. HP, BEAZLEY, HACKLORE
And finally
Roses are red Violets are blue Poetry in prompts jailbreaks AI for you – POETIC JAILBREAKS